// 01
Electronics & Embedded Hardware
PCB validation, signal analysis, hardware troubleshooting, and product development built on measurable evidence.
Michael Bell // Cybersecurity Engineer
Attack like a Red Team. Defend like a Blue Team. Improve together through instrumentation, validation, and practical engineering.
$ ./initialize-purple-team-lab.sh
[OK] Wazuh SIEM connected
[OK] Suricata IDS streaming
[OK] Zeek telemetry active
[OK] corp.local endpoints online
Current objective
Turn attack behavior into actionable detection logic.
SYSTEM ONLINE_
I am an electronics hardware engineer transitioning into cybersecurity. My background spans hardware validation, firmware, enterprise systems, and the disciplined troubleshooting needed to understand how complex systems fail.
PCB validation, signal analysis, hardware troubleshooting, and product development built on measurable evidence.
Nineteen years working with C/C++, low-level systems, embedded code, and the boundary between hardware and software.
Hands-on ownership of a small enterprise network, including Windows systems, Active Directory, and operational support.
Applying engineering rigor to attack simulation, telemetry, detection logic, investigation, and defensive improvement.
A working environment for validating telemetry, reproducing attack paths, and turning observations into defensible controls.
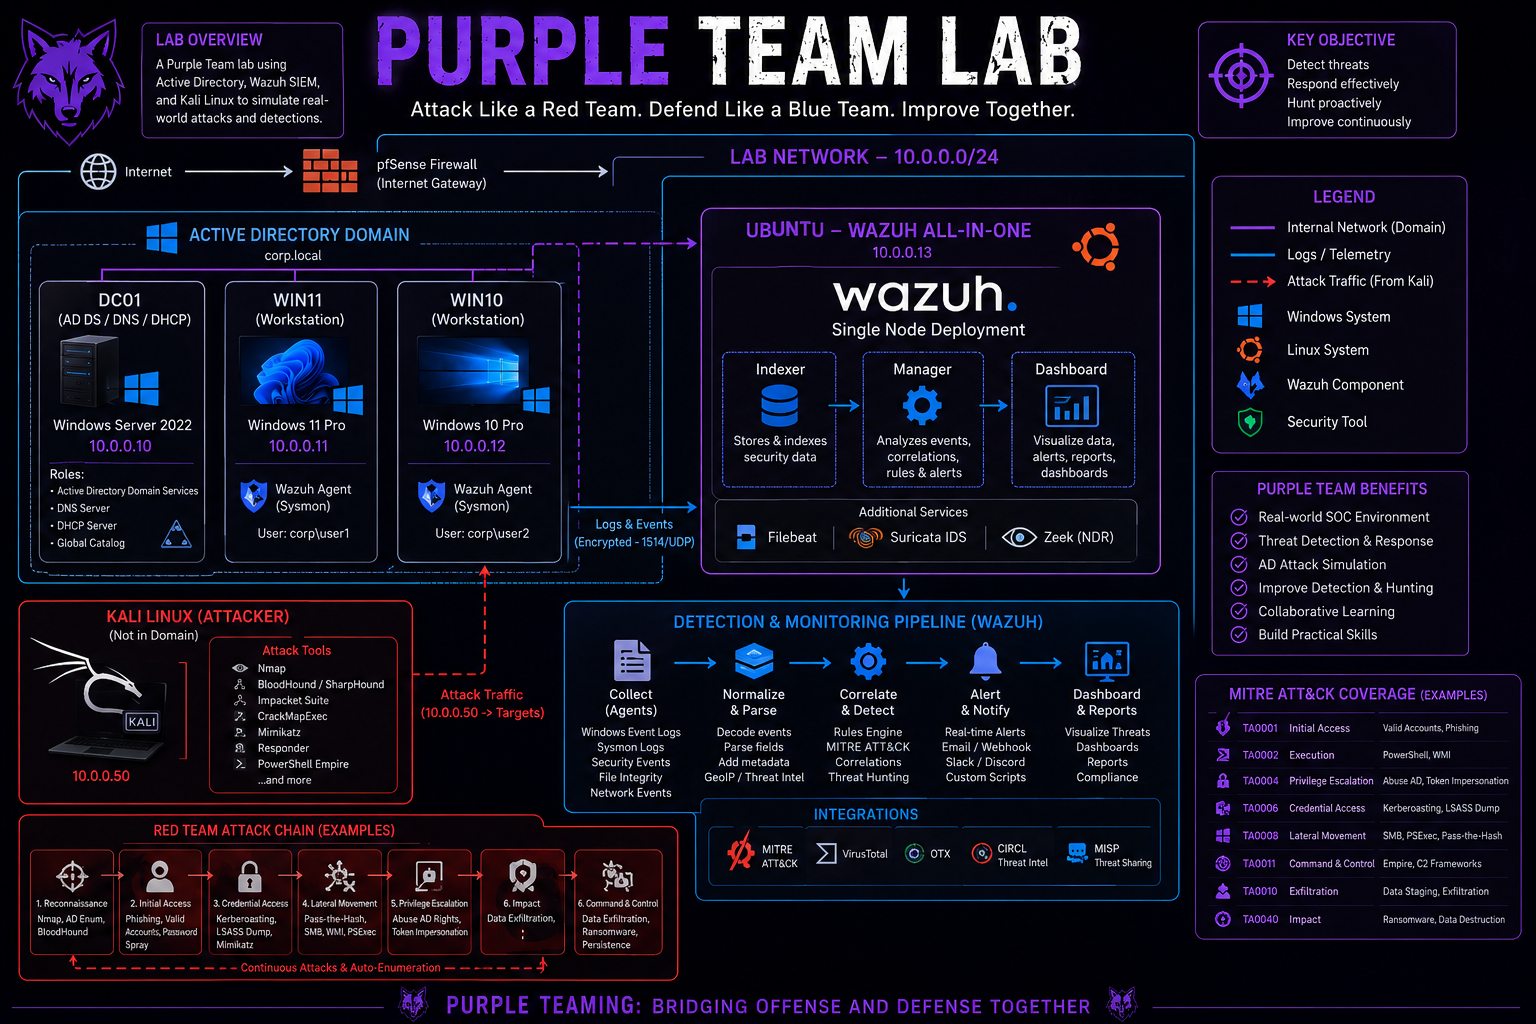
10.0.0.0/24
The control point for segmented lab traffic, internet access, and observation of attack paths across the environment.
SIEM, detection engineering, threat hunting, telemetry, and SOC operations.
Security architecture, vulnerability management, risk, and defensive controls.
Penetration testing, attack simulation, purple-team techniques, and learning labs.
Python, PowerShell, parsers, utilities, and practical security automation.
Wazuh, pfSense, Suricata, Zeek, and Windows telemetry in a working environment.
Cheat sheets, investigation guides, technical references, and lab notes.
Get-WinEvent -FilterHashtable @{LogName="Security"; Id=4625} | Select-Object TimeCreated, Messagesudo nmap -sV -O --script vuln 10.0.0.0/241999 to 2004
Completed
Electrical and Electronics Engineering Technology
Pennsylvania College of Technology
2020 to 2027
In progress
Information Technology, Cybersecurity Focus
Ira A. Fulton Schools of Engineering at Arizona State University
2020 to 2028
In progress
Information Technology, Cybersecurity Focus
Arizona State University
Open to cybersecurity engineering, threat hunting, detection engineering, and purple-team opportunities.
mike@ThreatHuntHQ:~$ open_channel --email